
Description
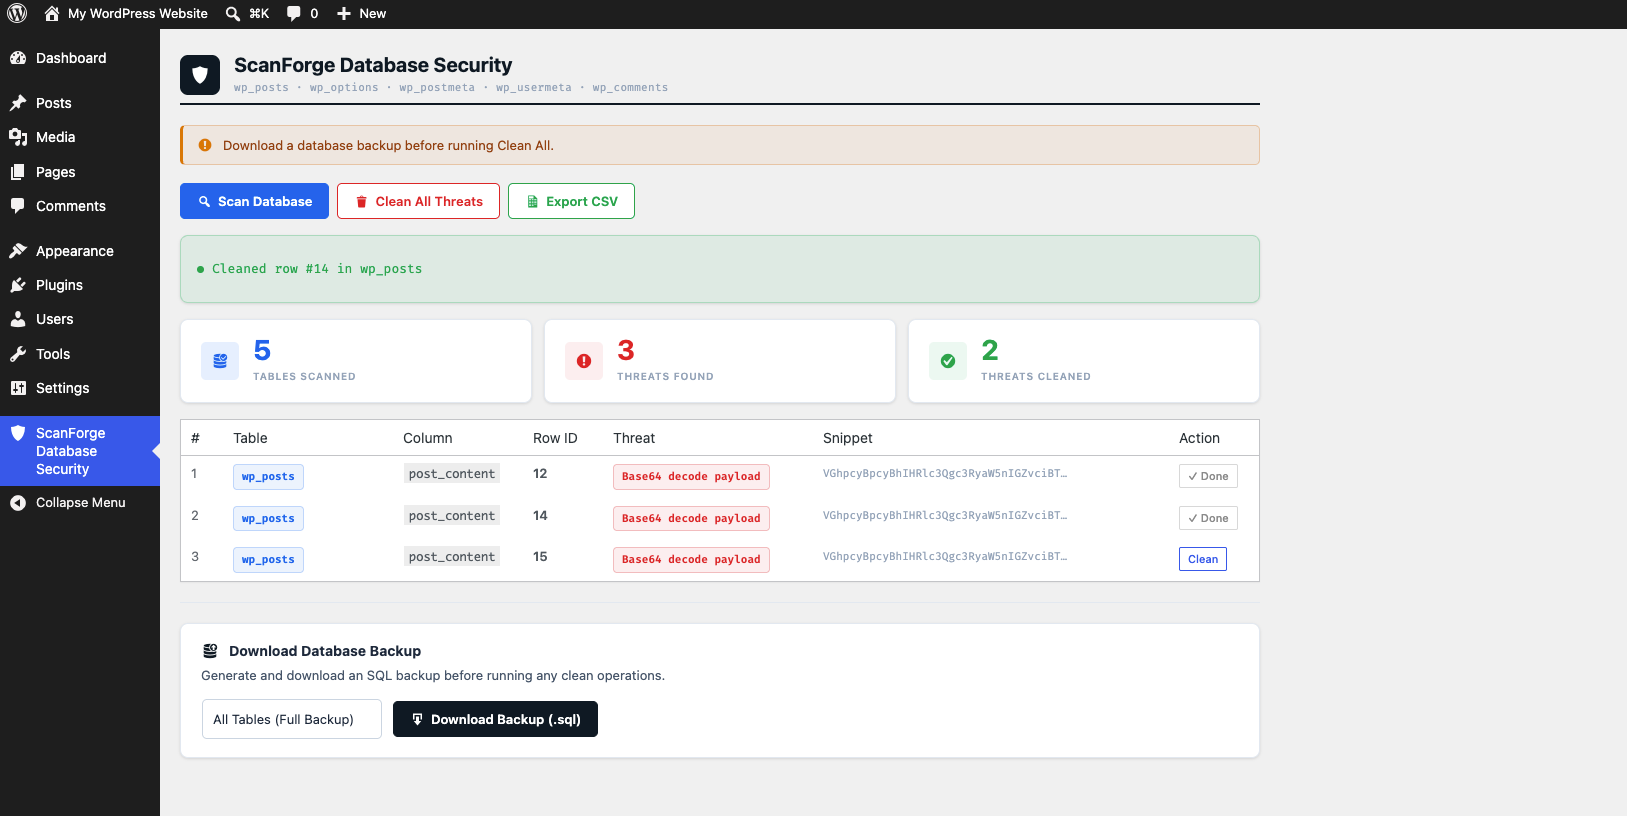
ScanForge Database Security helps WordPress administrators find and remove malicious code and spam injected into the database. It scans the most commonly attacked WordPress tables for known malware signatures such as traffic hijacking scripts, obfuscated PHP payloads and web shells, and it has a separate page for spam content such as gambling, pharmaceutical and SEO link spam.
Malware and spam are handled on two different pages, because they need different decisions: malware should be cleaned, while spam is content you may want to review before removing.
Features
- Scans wp_posts, wp_options, wp_postmeta, wp_usermeta, and wp_comments tables
- Malware Scanner page: detects 14 known malware signatures
- Spam Detection page: detects 34 spam phrases in 6 categories
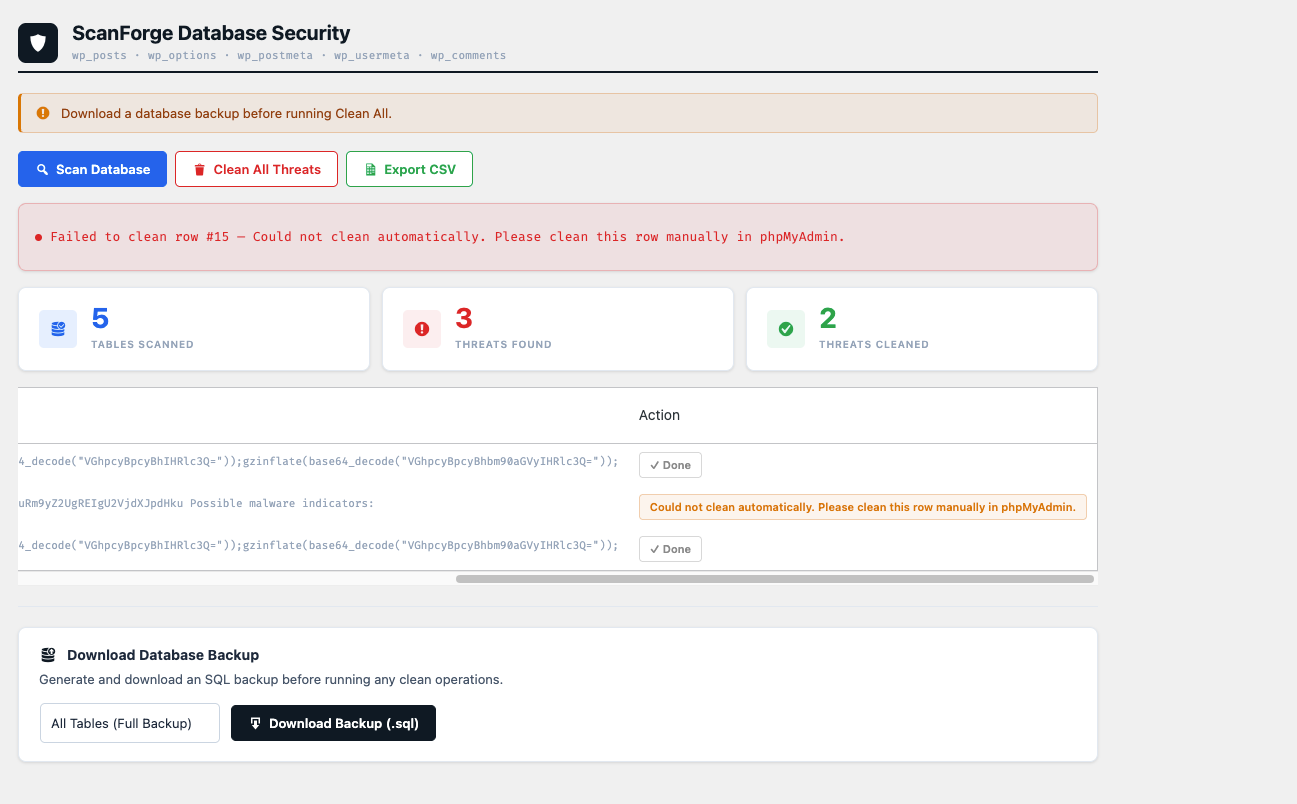
- Clean individual rows or all malware threats at once
- Delete spam one item at a time, or select several and delete them together
- Nothing is deleted automatically
- Download a database backup (.sql) before cleaning
- Export scan results as a CSV report
- Signature list is stored in an editable data file (data/patterns.json)
- Simple and easy to use admin interface
- No external service required — runs entirely on your server
- Follows WordPress coding standards
Detected Malware
- Traffic hijacking scripts
- Nulled plugin backdoors
- Obfuscated PHP injections using encoded or compressed payloads
- Dynamic script injections
- Tracking cookie injections
- Known malware loader functions
- Shell command execution attempts
- Known web shell signatures
Detected Spam
- Gambling and casino spam
- Pharmaceutical spam
- Adult spam
- Cryptocurrency spam
- Financial and loan spam
- SEO and backlink spam
Spam Detection and Deleting
The Spam Detection page lists every item that matches a spam phrase. You decide what to remove:
- Posts are moved to the Trash, so you can restore them if a result was a false positive
- Comments, post meta, user meta and options are deleted permanently
- Core WordPress options (such as the site URL) can never be deleted from this page
- Each item is checked again just before it is deleted, and skipped if it no longer matches
Important Notice
This plugin helps clean database infections but it does NOT prevent reinfection if the source of the malware (such as nulled/pirated plugins or themes) is still installed. Always remove nulled software and use legitimate licensed plugins to permanently fix infections.
Spam detection is based on phrases, so a legitimate post that mentions one of them (for example an article about online casinos) can be listed. Always review each result before deleting, and take a backup first.
Usage
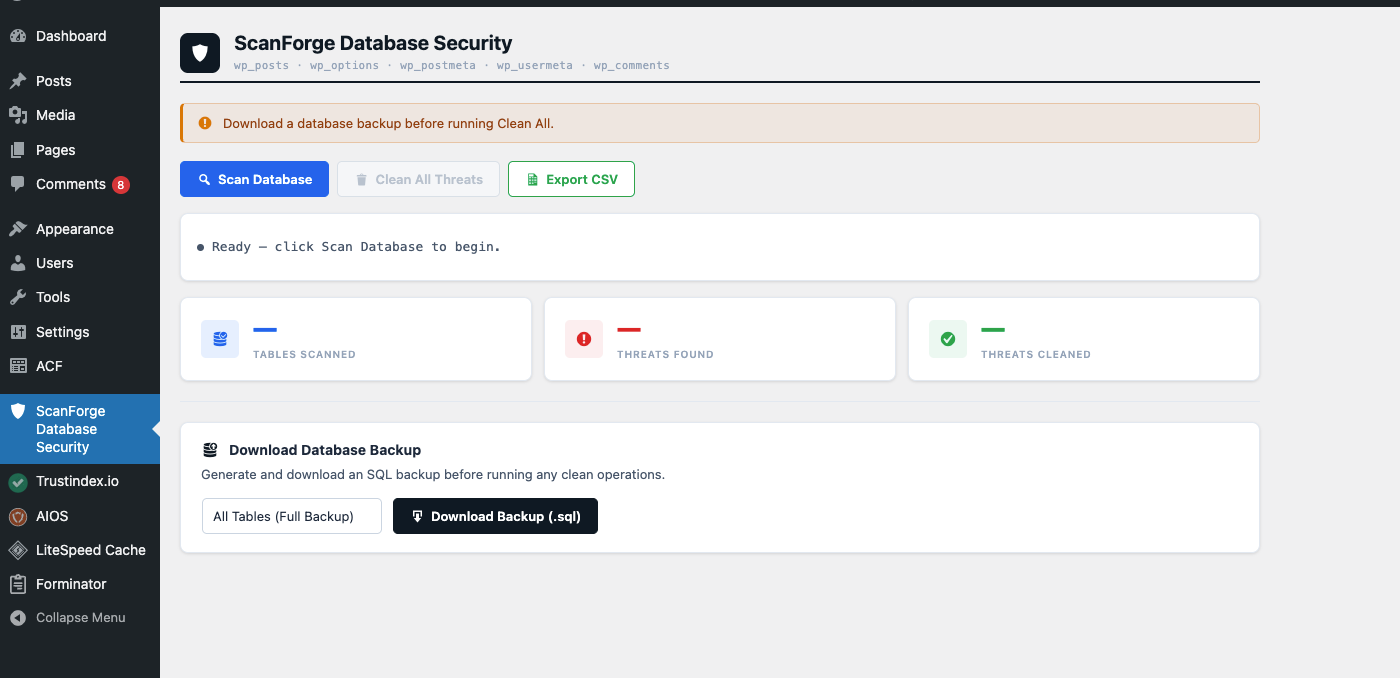
- Go to ScanForge Database Security > Malware Scanner in your WordPress admin menu
- Click Download Backup to save a copy of your database
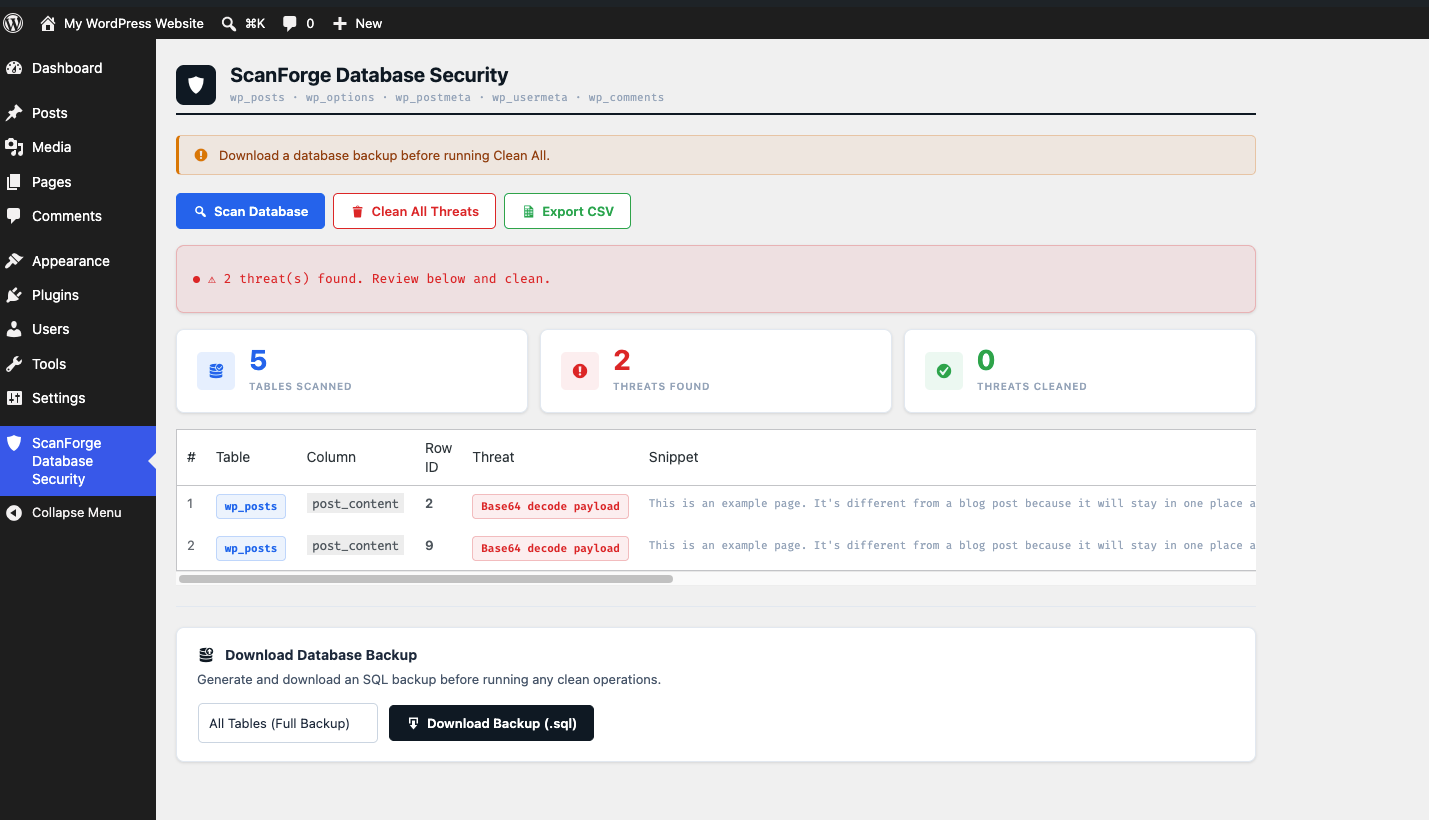
- Click Scan Database
- Review the threats found
- Click Clean All Threats or clean rows individually
- Export a CSV report if needed
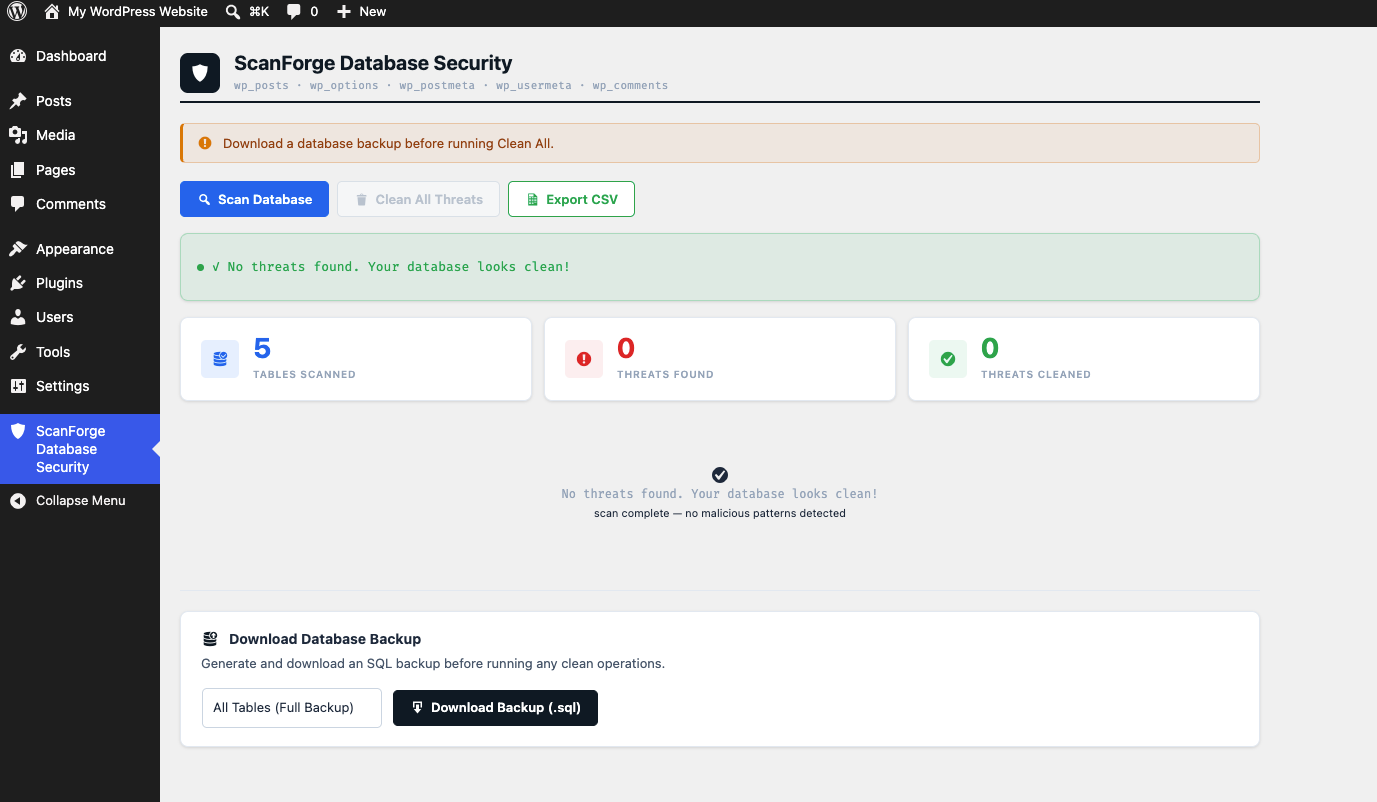
- Run the scan again to verify everything is clean
- For spam content, open ScanForge Database Security > Spam Detection, click Scan for Spam, and delete only the items you want removed
Screenshots

Installation
Automatic Installation
- Go to Plugins > Add New in your WordPress admin
- Search for “ScanForge Database Security”
- Click Install Now and then Activate
Manual Installation
- Download the plugin zip file
- Go to Plugins > Add New > Upload Plugin
- Upload the zip file and click Install Now
- Click Activate Plugin
After Installation
Navigate to ScanForge Database Security in your WordPress admin sidebar to start scanning.
FAQ
-
How do I run a database security scan?
-
Simply navigate to the plugin menu in your WordPress dashboard and click “Scan Database” to instantly scan your database tables for malware.
-
Will this plugin prevent future infections?
-
No. This plugin cleans existing infections. To prevent future infections you must remove all nulled/pirated plugins and themes, keep all software updated, and use a firewall plugin like Wordfence.
-
Is it safe to use Clean All?
-
Always take a full database backup before using Clean All. The plugin removes malicious script blocks while preserving your legitimate content, but a backup is always recommended.
-
What tables does it scan?
-
It scans: wp_posts, wp_options, wp_postmeta, wp_usermeta, and wp_comments.
-
Can I export the scan results?
-
Yes. After scanning, click the Export Report button to download a CSV file of all threats found.
-
Does it work with custom table prefixes?
-
Yes. The plugin uses WordPress’s $wpdb object which automatically handles custom table prefixes.
-
Where is the spam scanner?
-
Spam has its own page: ScanForge Database Security > Spam Detection. It is not mixed into the Malware Scanner results.
-
Does the plugin delete spam automatically?
-
No. Spam is only listed. You choose which items to delete, one by one or with “Delete Selected”.
-
Can I restore something I deleted from the Spam Detection page?
-
Posts are moved to the Trash, so you can restore them from Posts > Trash. Comments, post meta, user meta and options are deleted permanently, so take a database backup before deleting.
-
Why was one of my normal posts listed as spam?
-
Spam detection looks for phrases such as “online casino”. A genuine article that uses one of these phrases can be listed. Review each result and only delete what is really spam.
-
What is the data/patterns.json file?
-
It holds the malware signatures and spam phrases that the scanner looks for. If the file is missing or damaged the plugin refuses to scan and shows an error, so it can never report a falsely clean database. Reinstall the plugin to restore it.
Reviews

Contributors & Developers
“ScanForge Database Security” is open source software. The following people have contributed to this plugin.
Contributors
Translate “ScanForge Database Security” into your language.
Interested in development?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Changelog
1.0.0
- Initial release
- Scan wp_posts, wp_options, wp_postmeta, wp_usermeta, wp_comments
- Detect 15+ malware patterns
- Clean individual rows or all threats
- Export CSV report
1.0.1
Added compatibility with PHP 7.0
1.0.2
Added single-table scanning functionality
Added “Scan All Tables” option for scanning the entire database
Improved scan performance and usability
1.0.3
- Added Wordfence compatibility.
- Added Elementor compatibility.
- Added Gravity Forms compatibility.
- Added Slide Security exclusions.
- Fixed minor bugs and improved overall stability.
1.0.4
Improved scan performance and usability.
1.0.5
- Added gambling, casino, betting, pharmaceutical, adult, cryptocurrency, financial, and SEO spam injection detection.
- Added detection for common gambling and casino spam phrases, including online casino, sports betting, betting bonuses, free spins, and related content.
- Improved detection of common pharmaceutical, adult, cryptocurrency, financial, and backlink/SEO spam injections.
- Improved spam detection coverage while using targeted phrases to help reduce false positives.
- Improved scan performance and usability.
1.0.6
- New “Spam Detection” submenu page — spam is no longer mixed into the Malware Scanner results.
- Gambling, pharmaceutical, adult, cryptocurrency, loan and SEO/backlink spam phrases are scanned only on the new page.
- Nothing is removed automatically: delete a single item, or tick several and use “Delete Selected”.
- Posts are moved to Trash (restorable); comments, post/user meta and options are deleted permanently. Core WordPress options are protected.
- Each row is re-checked just before deletion and skipped if it no longer matches a spam phrase.
- Fixed a duplicate spam phrase entry and a stale-cache issue after cleaning a row.
1.0.7
- Spam Detection: deleted items now disappear from the results table straight away, and the “Spam Items Found” count shows how many are still left.
- Spam Detection: fixed a bug where the last deleted row could stay on screen after deleting.
- Spam Detection: the results table now fits the screen width, and long descriptions wrap over several lines instead of being cut off.
- Malware signatures, spam phrases and cleaner rules now live in
data/patterns.jsoninstead of being written out in PHP code. Signatures are stored as fragments, so security tools no longer flag the plugin’s own detection list. - The scanner now refuses to run, and says why, if the signature file is missing or damaged, so a broken install can never report a falsely clean database.
- Scan result labels no longer spell out function names and domains.
- Removed
set_time_limit()calls and fixed a WordPress coding-standards error in the scanner database query. - The plugin scripts and styles now reload automatically after an update, so an old cached copy is never used.
- Readme: shorter short description, plus new Spam Detection and signature file documentation.